Blog

  • 3D Secure Explained: Why Your Bank Asks for Codes Online

    3D Secure Explained: Why Your Bank Asks for Codes Online


    Example scenario: you’re paying for a software plan, the checkout page goes gray and a box from your bank asks for a code sent by text. The text never comes. You request another, the box times out, and the merchant shows “3D Secure verification failed.” Your card has money on it and works in shops, so what went wrong?

    3D Secure is the extra check behind those bank pop-ups and app prompts. Most of the time you never see it. When you do and it fails, the error message rarely explains why. This guide covers how 3D Secure works, the common reasons a 3D Secure check fails, a step-by-step fix list, and when to stop retrying and call your bank.

    What 3D Secure is

    3D Secure (3DS) is an authentication standard for online card payments. The card networks run their own programs on it: Visa Secure, Mastercard Identity Check and American Express SafeKey. Its job is to confirm that the person paying is the cardholder before the payment is authorized. In Europe and the UK, strong customer authentication rules mean many online payments must be verified this way, so European shoppers see it often.

    How a 3D Secure check works

    Three parties are involved: the merchant, the card network’s 3DS system, and your bank (the issuer). As Visa’s guide to how 3D Secure works describes, the merchant sends transaction details through the network to your bank, which assesses the risk using data such as device type, location and spending patterns. Then one of two things happens:

    • Frictionless flow: the bank judges the payment low-risk and approves the authentication in the background. You see nothing.
    • Challenge flow: the bank wants more proof and asks you to verify, usually with a one-time code, approval in your banking app or biometrics.

    Why your bank asks more often sometimes

    Challenges are more likely when a payment looks different from your usual pattern: a new merchant, a larger amount, a foreign currency, a new device or browser, or a different country from your normal one. A run of challenges doesn’t mean something is wrong with your card. It means your bank is being careful.

    Why 3D Secure fails

    CauseWhat you seeFix
    Code sent to an old phone numberNo text arrivesUpdate your mobile number with the bank, then retry
    Banking app not set up for approvalsPrompt says to approve in app, nothing appearsOpen the app, sign in, enable notifications or approvals
    Code typed wrong or expired“Authentication failed” after entering the codeRequest a new code and enter it promptly
    Too many failed attemptsVerification is blocked or every try failsWait, then contact your bank to reset
    Pop-up blocked or extension interferingBlank or frozen verification windowDisable blockers for the site or try another browser
    Session timed outBox closes before you finishHave your phone ready and restart checkout
    Bank or network outageErrors at several merchants at onceWait and retry later
    Bank declined the payment on risk groundsVerification passes but payment is declinedCall the bank to confirm it was you
    Card doesn’t support 3D SecureMerchant rejects the card at verificationAsk your issuer, or use another card

    Step-by-step: what to do when 3D Secure fails

    1. Check the basics. Re-enter the card number, expiry, security code and billing address exactly as your bank has them.
    2. Get your phone ready first. Have it in hand, open your banking app and make sure you have signal before you press pay.
    3. Turn off pop-up and ad blockers for the checkout. The verification window often runs in a frame that blockers interrupt. A private window without extensions is a quick test.
    4. Request a fresh code once. Use only the most recent code. Older codes usually stop working when a new one is sent.
    5. Stop after two or three tries. Repeated failures can lock verification for that card. Retrying ten times makes things worse.
    6. Check your bank’s app for messages. Many banks show a pending approval or a fraud alert there, even when a text doesn’t arrive.
    7. Call your bank. Ask whether the attempt was blocked, whether your phone number is current and whether your card is enrolled for online authentication.
    8. Try another payment method if it’s urgent. A wallet such as Apple Pay or Google Pay, or a different card, can get you through while the bank fixes the issue.

    What not to do

    • Never share a code with anyone who contacts you. A real bank will not ask you to read out a verification code. Codes you didn’t request mean someone may have your card details.
    • Don’t look for cards that skip verification. Avoiding 3D Secure removes a fraud protection and often breaks the merchant’s rules. Fix the authentication instead.
    • Don’t keep retrying across several cards in a row. Rapid attempts look like fraud to merchants and can get your account flagged.

    Is 3D Secure worth the hassle?

    For shoppers, yes. It makes stolen card details much harder to use online, and most payments pass without any visible step. Its limits are worth knowing, though. It confirms that you are the cardholder; it does not check whether a shop is honest. If you approve a payment to a scam site, 3D Secure has done exactly what it was designed to do. And it isn’t applied to every transaction, so it is one layer of protection among several.

    3D Secure and prepaid virtual cards

    Prepaid and virtual cards also go through 3D Secure when the issuer supports it, which many merchants now expect for online payments. When you choose a prepaid card, check that the provider supports 3D Secure, especially for subscriptions and software.

    Vizovcc, for example, says every card it sells supports 3D Secure. Its prepaid virtual cards are bought with crypto from an account balance, and each card’s details appear in your dashboard once it is ready. If a payment fails, the cause is often simpler than 3DS: the balance doesn’t cover the charge plus tax, or the card is frozen. The dashboard lets you freeze and unfreeze cards, so it is worth checking that first. Vizovcc’s decline checklist for subscription cards walks through those checks: confirm the balance, confirm the card isn’t frozen, re-enter details carefully and wait before retrying.

    Two honest points. Even with 3D Secure, any merchant can decline a prepaid card, so no provider can promise acceptance. And Vizovcc card purchases are final, so read the card page for currency and balance before buying. If verification keeps failing on a Vizovcc card, contact its support through live chat, WhatsApp, Telegram or email rather than retrying repeatedly.

    Frequently asked questions

    Why didn’t I get my 3D Secure code?

    The most common reasons are an outdated phone number on your bank account, weak signal, or a bank that now uses app approvals instead of texts. Check your banking app, then call the bank.

    Is “3D Secure failed” the same as a declined card?

    No. A 3D Secure failure means the identity check didn’t complete. A decline means the bank refused the payment itself. You can pass 3D Secure and still be declined, for example for insufficient funds.

    Can I turn 3D Secure off?

    Generally no. Whether a check is required is decided by the merchant, the network and your bank, not by the shopper.

    Does 3D Secure cost anything?

    Not for shoppers. There is nothing to download or sign up for beyond your bank’s normal app or text verification.

    Key takeaways

    • 3D Secure confirms you are the cardholder; most payments pass in the background.
    • Failures usually come from outdated phone numbers, app settings, blockers, timeouts or too many attempts.
    • Stop after a few tries and call your bank instead of retrying repeatedly.
    • Never share verification codes, and never look for ways around the check.
    • Prepaid virtual cards that support 3D Secure, such as Vizovcc’s, still need enough balance and an unfrozen card.

    Before your next big online payment, check that your bank has your current phone number and that app approvals are switched on. If you are looking for a prepaid card that supports 3D Secure for subscriptions, take a look at Vizovcc and read each card page before you buy.

  • Expense Cards for Contractors: A Card That Ends With the Job

    Expense Cards for Contractors: A Card That Ends With the Job

    Here is an example many small agencies will recognize. You bring in a freelance video editor for an eight-week project. In week one they need stock footage, a music license and a month of a cloud storage plan. You have two easy choices: let them pay and add the costs to their invoice, or send them the company card number. The first means waiting on receipts and checking markups. The second means that, eight weeks later, a person who no longer works with you still has a working company card number saved in their browser.

    Contractors and temporary staff need to spend money on your behalf, but they sit outside most of the systems that manage employee spending. This guide covers the options for a contractor expense card, how to set one up so it stays tied to the contract, and how to retire it cleanly when the work is done.

    Why contractors need a different approach

    • Short tenure. A contract may last weeks. Whatever access you grant has to be undone soon, and often by someone other than the person who granted it.
    • Outside HR systems. Contractors usually aren’t in the HR platform, so the automatic offboarding steps that cover employees don’t run for them.
    • Several clients at once. A freelancer may be juggling work for many companies. Your card number is one of many saved payment methods on their devices.
    • Classification sensitivity. How much control you take over a worker’s job, including their expenses, is one of the factors tax authorities look at when deciding whether someone is a contractor or an employee.

    Five ways to cover contractor expenses

    OptionUpfront cost to contractorCompany visibilityClean-up at contract end
    Contractor pays and bills the cost on their invoiceFull amount until you pay the invoiceLow: one invoice line per monthNone, but subscriptions may stay in their name
    Reimbursement against receiptsFull amount until reimbursedMedium: receipts arrive lateMove any subscriptions off their personal card
    Shared company cardNoneLow: mixed with everyone’s chargesReplace the card everywhere it is saved
    Company buys on requestNoneHighNone, but slow for urgent purchases
    Dedicated card per contractorNoneHigh: every charge on the card is theirsRetire one card

    For contractors who make more than a handful of purchases, a dedicated card is usually the cleanest choice. Every charge on it belongs to one person and one contract, and ending it doesn’t affect anyone else.

    Don’t rely on the expiry date

    A common idea is to give a contractor a card that expires when the contract ends. Some corporate card programs let you set a custom expiry, but many cards, including most prepaid cards, carry a fixed expiry measured in years. Contracts also change: they get extended, paused or ended early. An expiry date set at kickoff is often wrong by the end.

    A more reliable approach is to treat the card as part of the contract and retire it as a step in the contract’s closing checklist. That works with any card, whatever its expiry.

    Setting up a contractor expense card, step by step

    1. Write allowable expenses into the contract. List what the company pays for directly (software, licenses, materials, travel) and what the contractor covers from their fee.
    2. Set the project expense budget. Agree an amount for the whole contract or per month, and who approves anything above it.
    3. Issue one card for this contractor only. Never reuse a card from a previous contractor, and never share one between two people.
    4. Use company accounts where possible. If the contractor needs a tool, create it under a company email and add them as a user. Save the card to the company account yourself, so the contractor uses the tool without handling the card number.
    5. Share card details securely when you must. Use a business password manager with access for that one person, not chat or email.
    6. Record the card in a register. Last four digits, contractor name, contract reference, start date, planned end date and budget. Keep full numbers and CVVs out of it.
    7. Review charges every two weeks. Short contracts leave little time to catch problems at month end.

    The contract-end checklist

    1. Remove the card from every site and tool where it is saved.
    2. Cancel subscriptions the project no longer needs, or move them to a long-term company card.
    3. Remove the contractor’s user access from company tools and ad accounts.
    4. Collect any missing receipts and reconcile the card against the project budget.
    5. Mark the card as retired in the register, with the date.
    6. If the card details were ever shared with the contractor and a subscription has to keep running, buy a new card for it rather than leaving the old number in use.

    Which option fits the contract?

    • One or two small purchases in total: let the contractor bill them as pass-through costs on the invoice.
    • Regular purchases over several weeks: issue a dedicated card and close it with the contract.
    • Large or one-off purchases, such as equipment: buy them directly in the company’s name.
    • Long-running contract that behaves like a role: review whether the arrangement is still a contract at all.

    A note on worker classification

    Paying for a contractor’s work expenses is normal, but it isn’t neutral. In the US, the IRS guidance on contractors versus employees lists financial control, including whether expenses are reimbursed and who provides tools and supplies, as one of the categories it considers. A company card for project costs doesn’t decide the question on its own, but it is one factor among many. Keep the card scoped to project costs agreed in the contract, and ask your advisor if you are unsure. Other countries apply their own tests.

    Example: one prepaid card per contractor with ZenVCC

    ZenVCC is a prepaid virtual card platform that suits the dedicated-card model. You fund one company balance with crypto (Bitcoin, USDT on TRC-20 or Solana, TRX or SOL), each deposit is checked on its blockchain before it is credited, and you buy a separate prepaid Visa, Mastercard or American Express card for each contractor or project.

    How it maps to the steps above:

    • A fixed ceiling. A prepaid card can’t pay more than its balance, so the contractor can’t overspend the card.
    • Low cost per card. Each card has a one-time $10 issue fee on top of its price, $0.10 per payment and no monthly fee, so a card for an eight-week contract doesn’t leave a recurring cost behind.
    • Retire by process, not by expiry. Cards are valid for three years from the day they are ready, so the expiry won’t match a contract end date. Close each card with the checklist above.

    Know the limits too. ZenVCC has no freeze button or per-card spending limit, and there are no team roles or sub-accounts: whoever signs in sees every card. Contractors should never get the login. Keep it with one person in the company, who adds cards to company tool accounts or shares a single card’s details through a password manager. If a contractor’s card details ever end up in the wrong place, ZenVCC’s advice on what to do when card details leak is to remove the card from every site where it is saved and buy a new card for those payments, which matches the contract-end checklist.

    Mistakes to avoid

    • Passing a card from one contractor to the next. Charges from two people on one card can’t be cleanly separated.
    • Letting contractors open tools in their own name. When they leave, you lose the account, the data and the cancel button.
    • Skipping the closing checklist because the card “expires anyway.” Most cards outlive the contract by years.
    • Paying for things outside the contract. Personal or non-project costs blur both your books and the working relationship.

    Key takeaways

    • Contractors need spending access, but they fall outside the systems that clean up employee access.
    • A dedicated card per contractor keeps every charge attributable and makes the exit simple.
    • Don’t count on the card’s expiry date. Retire the card as part of the contract’s closing checklist.
    • Keep tools in company accounts and card numbers away from contractors where you can.
    • Scope the card to project costs written into the contract.

    Before your next contractor starts, add two lines to the contract template: allowable expenses and the card’s retirement step. If you want a prepaid card per contractor with no monthly fee, take a look at ZenVCC and see whether it fits how you run contracts.

  • Shadow IT Is a Finance Problem: Find Every Software Charge

    Shadow IT Is a Finance Problem: Find Every Software Charge

    Consider an example that plays out in many mid-sized companies. During an annual security review, IT finds three different file-sharing tools holding customer documents. None of them went through procurement. One was expensed by a sales manager who left last spring, and it renewed last month for a full year on a card that still works. Nobody in IT knew it existed. Finance had the charge all along, coded as “Software, misc.”

    Shadow IT, meaning software and cloud services used without IT’s knowledge or approval, is usually treated as a security issue. It is one. But nearly every unapproved tool has to be paid for, which means it leaves a trail in finance data before it shows up anywhere else. This guide explains where shadow IT spend hides, how finance and IT can find it together, and how routing software purchases through known cards keeps it from coming back.

    Why shadow IT starts in the books

    Most SaaS tools are sold with a credit card and a sign-up form. A team lead with a deadline and a budget doesn’t need IT to start a trial, and once the trial converts, the tool becomes part of how the team works. The purchase decision happens at the card, so the card data is where you can see it.

    That makes finance the natural partner for discovery. IT knows which tools are approved and what risk they carry. Finance knows what is being paid for. Neither list is complete without the other.

    Where shadow IT spend hides

    • Expense reports. A software subscription paid on a personal card and reimbursed as “office supplies” or “misc.”
    • Shared company cards. One card used by a whole department, with charges coded by whoever does the books that month.
    • Free trials that convert. A trial started with a card turns into a paid plan, often annual, without a second decision.
    • In-app upgrades and add-ons. An approved tool picks up paid seats, storage or AI features added by users with billing rights.
    • Cloud marketplaces. Third-party software billed through a cloud provider’s invoice, where it looks like infrastructure spend.
    • Departmental budgets. Marketing, sales and engineering often buy their own tools from their own budget lines.

    Discovery methods compared

    No single source finds everything. The useful question is what each one misses.

    MethodWhat it findsWhat it missesWho runs it
    Card and expense data reviewAnything paid for, including tools IT has never seenFree tools and tools paid by another companyFinance
    Single sign-on (SSO) logsApps connected to company identityAnything signed up with a password or personal emailIT
    Network or browser monitoringWeb apps people visit on managed devicesPersonal devices, and whether the app is paidIT or security
    Vendor invoices in accounts payableTools on formal contractsCard and expense purchases, which is where most shadow IT sitsFinance
    Team surveysTools people remember and are willing to mentionAnything forgotten or deliberately left outIT with managers

    Card and expense data is the cheapest place to start, because finance already has it. Security frameworks treat this as basic hygiene: CIS Control 2 calls for an active inventory of all software so that unauthorized software can be found and dealt with.

    A step-by-step plan to find and stop shadow IT spend

    1. Pull 12 months of card and expense data. Include company cards, reimbursed expenses and accounts payable. Filter for software, SaaS, cloud and app-store merchants, plus anything coded to vague accounts.
    2. Build the inventory. One row per tool: vendor, monthly or annual cost, renewal date, payment method, who pays and who uses it.
    3. Find an owner for every tool. If nobody claims it, that is useful information too. Unclaimed tools go to the top of the review list.
    4. Review with IT. For each tool, decide: approve, consolidate into an existing tool, or cancel. Check what data each tool holds before cancelling.
    5. Create a simple request path. A short form or ticket for new software, with a promised response time. People bypass IT when approval is slow, not because they enjoy it.
    6. Move approved tools onto known cards. Pay each approved vendor from a card the company controls, ideally one card per vendor, under a company billing email.
    7. Close the expense-report route. Make software reimbursement an exception that needs IT sign-off. When the approved path is faster, this rule rarely has to be enforced.
    8. Review new merchants monthly. Any software merchant that appears on a card or expense report without an inventory row is a new shadow IT candidate.

    What card controls can and can’t do

    Many corporate card programs offer controls such as per-card spending limits, merchant category restrictions and approval workflows. These help, but the bigger gain comes from structure: when every approved tool has its own card, the card becomes the tool’s ID. A software charge on any other card, or on an expense report, stands out immediately.

    Controls also have limits. They can’t tell you whether a tool is safe, whether its data is backed up or whether a cheaper approved tool already does the job. That is IT’s review. Cards give finance the visibility; the decision still needs both teams.

    A quick triage guide for each tool you find

    • Holds customer or employee data and has no owner: secure the data, export it, then cancel.
    • Duplicates an approved tool: move the users across and cancel at renewal.
    • Used by several people and does something no approved tool does: run it through the request path and approve it properly.
    • Used by one person, low cost, no sensitive data: approve or cancel quickly. Don’t spend more time reviewing it than it costs.

    Example: one card per approved vendor with ZenVCC

    ZenVCC is a prepaid virtual card platform that fits step 6 of the plan. A company funds one balance with crypto (Bitcoin, USDT on TRC-20 or Solana, TRX or SOL), each deposit is checked on its blockchain before it is credited, and you buy a separate prepaid Visa, Mastercard or American Express card for each approved vendor. Its service page recommends exactly this pattern: a separate card per vendor, so every charge on a card belongs to one vendor, and when you stop using a service, you stop using its card.

    What it adds to a shadow IT program:

    • No monthly fee. Each card has a one-time $10 issue fee on top of its price and costs $0.10 per payment, with $0 a month, so a card for each small approved tool doesn’t add recurring overhead.
    • A hard ceiling. A prepaid card can’t pay more than its balance, so a surprise upgrade can’t run up an open-ended bill.
    • Three-year validity. Cards are valid for three years from the day they are ready, which keeps renewals from failing on expired cards.
    • Refund if a card can’t be prepared. The full amount, issue fee included, returns to the balance.

    Be clear about what it doesn’t do. ZenVCC doesn’t offer merchant locks or per-card spending limits, so “one card per vendor” is a rule your team keeps, not one the card enforces. It has no team roles or sub-accounts either: whoever signs in sees every card, so the login should sit with the one person who owns software payments. Vendors also decide which cards they accept, and the provider’s own page notes that several major cloud and workspace providers refuse prepaid or virtual cards, so check each vendor’s billing rules first. For the vendors that do accept them, separate cards for SaaS and cloud vendors make the monthly new-merchant review in step 8 fast.

    Mistakes to avoid

    • Treating discovery as a one-time audit. New tools appear every month. Make the merchant review a standing task.
    • Cancelling before checking data. A tool nobody approved may still hold the only copy of important files.
    • Punishing people who used shadow tools. They were solving a real problem. Fix the request path so they don’t need to again.
    • Leaving billing on personal emails. When the buyer leaves, so does access to the invoices and the cancel button.

    Key takeaways

    • Almost every shadow IT tool is paid for, so finance data is the fastest place to find it.
    • Combine card and expense reviews with SSO logs and IT knowledge; each source misses something.
    • Give every approved tool an owner, a company billing email and its own card.
    • A faster request path does more to stop shadow IT than a stricter rule.
    • Review new software merchants every month, not once a year.

    Start this month with a single export: 12 months of card and expense lines filtered for software merchants. Share it with IT and see how many tools are new to both of you. If you want a prepaid way to give each approved vendor its own card with no monthly fee, take a look at ZenVCC.

  • Canceled but Still Charged? Your Rights and How to Stop It

    Canceled but Still Charged? Your Rights and How to Stop It

    Take this example. In January you cancel a streaming plan, see a “sorry to see you go” screen and forget about it. In March, the same $15.49 charge appears on your card. Then it appears again in April. You are sure you canceled, but you never saved the confirmation, and the company’s help page sends you in circles.

    Being charged after you cancel is one of the most common billing complaints, and it is fixable. The order matters, though. Start with your rights, because they are what get your money back. Then fix the cause, and only then add the safeguards that make it hard for this to happen again.

    Your rights come first

    The rules below describe the United States. If you live elsewhere, your national consumer agency publishes the equivalent rights, and they are often just as strong.

    If you paid by credit card

    Under the Fair Credit Billing Act, you can dispute billing errors with your card issuer, including charges for things you did not accept or that were not delivered as agreed. Timing is strict: as the FTC’s guide to disputing credit card charges explains, your letter must reach the issuer within 60 days after the first bill with the error was sent to you. Write to the billing-inquiry address, not the payment address. The issuer must acknowledge your dispute within 30 days and resolve it within 90.

    If you paid by debit card or bank transfer

    You can withdraw a company’s permission to take automatic payments. According to the CFPB’s steps for stopping automatic payments, you tell the company and then your bank that you have revoked authorization, and follow up both in writing. Payments the company takes after that are errors you can ask your bank to refund. Your bank may also offer a stop payment order, usually for a fee.

    Chargebacks through the card network

    When you dispute a charge, your issuer can raise a chargeback with the merchant through the card network. Networks have dispute categories that cover recurring charges after a cancellation. Your evidence, especially the cancellation date and any confirmation, decides how that goes.

    Rules on automatic renewals

    The federal Restore Online Shoppers’ Confidence Act requires online sellers of recurring plans to provide a simple way to stop the charges. The FTC’s broader “click-to-cancel” rule was struck down by a federal appeals court in July 2025 before it took effect, but many states have their own automatic renewal laws that still apply.

    Why charges continue after you cancel

    Before you dispute anything, find the likely cause. It shapes what you say to the merchant and to your bank.

    • The cancellation never completed. Many flows have a retention offer or a final “confirm” button. Closing the page early leaves the plan active.
    • You canceled in the wrong place. A plan bought through an app store must be canceled there. Deleting the app does nothing.
    • It was a different account. A second login, an old email address or a family member’s plan can all bill the same card.
    • The charge covers an earlier period. Some services bill in arrears or charge a final usage invoice after cancellation.
    • An annual plan renewed. You canceled a monthly add-on but not the yearly base plan.
    • Your new card was updated automatically. Many issuers take part in network card-updater services that pass a replacement card’s details to merchants that held the old one. Replacing a card does not cancel a subscription.
    • It is a pending authorization. A temporary hold may drop off without becoming a charge.
    • It is a billing error. Sometimes the merchant simply got it wrong.

    What to do, step by step

    1. Collect your evidence. Find the cancellation email, a screenshot or the date you canceled. Check your inbox and the account’s billing history.
    2. Identify the charge. Confirm it is posted, not pending, and work out which period it covers and which account it came from.
    3. Contact the merchant in writing. Give the cancellation date, ask for the plan to be closed and request a refund of every charge after that date. Keep a copy.
    4. Dispute with your card issuer if the merchant does not fix it. For credit cards, write within the 60-day window. For debit cards, report it to your bank promptly and keep the dates.
    5. Revoke authorization to stop future charges. Tell the merchant and your bank in writing that the merchant may no longer charge you. Ask about a stop payment order or a merchant block.
    6. Check for card-updater carryover. If you replaced the card, ask your issuer whether the new number was shared with that merchant.
    7. Report patterns. If a company keeps charging people after cancellation, you can report it to the FTC or your state attorney general.

    Which tool solves which problem

    ActionCan get money backStops future chargesLimits
    Cancel with the merchantOnly if the merchant agreesYes, when completedYou need proof if it fails
    Dispute or chargeback with your issuerYes, if the dispute succeedsNo, on its ownDeadlines apply, and evidence decides the outcome
    Revoke authorization with your bankLater charges count as errorsYesDebit card charges can be harder for banks to block
    Stop payment order or merchant blockNoUsuallyFees may apply, and coverage varies
    Replace the card numberNoNot always, because of card updatersEvery other service on that card needs updating
    Separate prepaid card for the subscriptionNoLimits how much can be taken to the funds on the cardDispute options depend on the card provider

    Preventing it next time

    • Save every cancellation confirmation. Make a folder in your inbox for them. It is the single most useful piece of evidence in a dispute.
    • Cancel where you subscribed. App store plans in the app store, website plans on the website.
    • Set a reminder before trial and renewal dates. Trial terms still apply, so cancel a few days early.
    • Keep subscriptions off your main bank card. If a merchant keeps billing, you want the damage to stay away from the account that pays your rent.
    • Give each subscription its own card. A statement with one merchant on it makes a stray charge obvious.

    A backstop, not a replacement: prepaid cards per subscription

    The last two habits are where a prepaid card can help. If a subscription sits on a prepaid card that holds only what you intend to spend there, a merchant that keeps charging after you cancel can only take what is left on that card. Your bank account is not on file with the merchant at all.

    ZenVCC is one provider of this kind of card, and it is worth being exact about what it does and does not do. ZenVCC does not offer a way to freeze or close a card from its dashboard, so it cannot switch a card off the way some bank apps can. Its FAQ also does not describe a dispute process for card charges, so ask its support before you count on one. Your rights against the merchant, and the steps above, still come first.

    What it does offer is a separate prepaid virtual card for each subscription, bought from one balance funded with crypto (Bitcoin, USDT on TRC-20 or Solana, TRX or SOL). Each card has a one-time $10 issue fee, each payment costs $0.10 and there is no monthly fee. Cards are valid for three years. A few terms matter for this use:

    • Size each card carefully. Card purchases are final once the details are ready, and there are no transfers from a card back to your balance.
    • Cards cannot be topped up from the dashboard. A card can only spend the funds it holds.
    • Track charges at the merchant. The dashboard does not list card payments, so use each service’s billing page and save its receipts.
    • Remove the card when you leave. Deleting it from the merchant account, after canceling, adds one more barrier.

    For the full details on balances and refunds, read ZenVCC’s FAQ on balances, refunds and card details.

    Key takeaways

    • Start with your rights: credit card billing disputes have a 60-day written window, and debit payments can be stopped by revoking authorization with the merchant and your bank.
    • Find the cause first. Incomplete cancellations, app store plans and card updaters explain many surprise charges.
    • Replacing your card does not cancel a subscription and may not stop the charges.
    • Save every cancellation confirmation, because it decides most disputes.
    • A prepaid card per subscription limits how much a merchant can take, but it is a backstop, not a substitute for canceling and disputing.

    If you are dealing with a charge right now, start with step 1 today and keep every message in writing. For future subscriptions, consider keeping them on cards that hold only what you plan to spend. ZenVCC is one prepaid option to compare against your bank’s tools.

  • Swan Valley Tours: Elegant Charters Introduces New Chauffeur-Driven Experiences From Perth

    Swan Valley Tours: Elegant Charters Introduces New Chauffeur-Driven Experiences From Perth

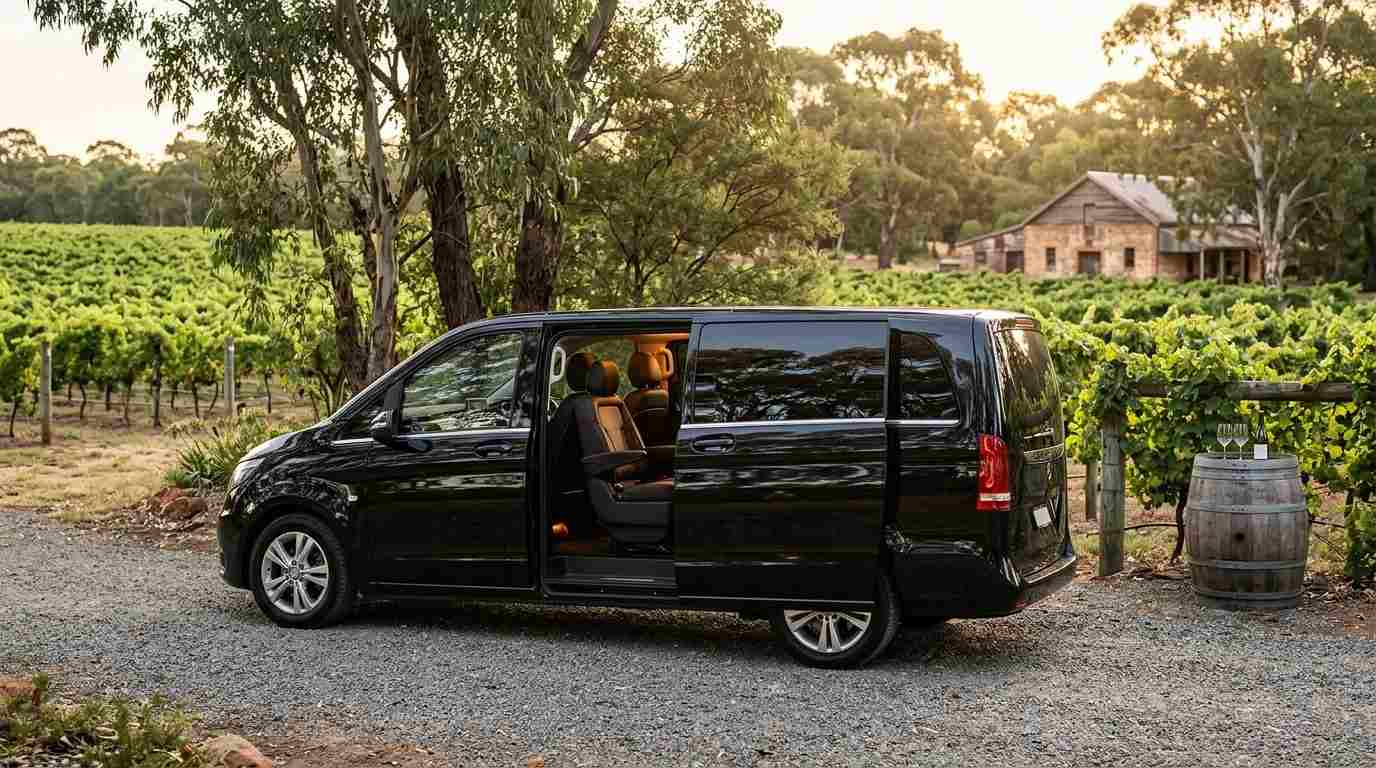
    Elegant Charters, a Perth-based chauffeur and passenger transport provider, is introducing a new Swan Valley Tours service designed to provide visitors and local travellers with convenient, private transportation to one of Western Australia’s well-known wine and tourism destinations.

    The new service adds another option to the company’s existing portfolio of airport transfers, corporate transportation, private tours and group travel services. It is intended for individuals, families and groups seeking a comfortable way to explore the Swan Valley without managing their own driving arrangements.

    Responding to the Demand for Convenient Regional Travel

    The Swan Valley, located northeast of Perth, attracts visitors interested in wineries, food producers, restaurants, local attractions and regional experiences. However, organising transportation can be an important consideration for travellers planning a full day of sightseeing, particularly those visiting multiple destinations.

    For visitors participating in wine-related activities, having access to a dedicated chauffeur service can provide an alternative to self-driving or coordinating multiple transport arrangements.

    Additional details are available at: https://share.google/gH9qsqNjtvVagBcyp

    Elegant Charters’ new Swan Valley Tours service addresses this transportation need by offering private travel options from Perth and surrounding areas.

    A Chauffeur Service Designed Around Different Travel Needs

    Elegant Charters provides a range of passenger transport options, with vehicles suited to different group sizes and travel requirements. Its fleet includes sedans, SUVs, four- to seven-seat vehicles, and minibuses and maxi cabs accommodating groups of approximately 13 to 24 passengers.

    These vehicle options allow the company to accommodate different types of travellers, from couples and families to larger private groups.

    The Swan Valley Tours service complements the company’s broader transportation offerings, which include Perth Airport transfers, corporate travel, wedding transportation, hotel transfers, cruise transport, FIFO transfers and long-distance journeys.

    Customers can also enquire about personalised travel arrangements based on their transportation requirements.

    Flexible Booking and Passenger Convenience

    In addition to its chauffeur services, Elegant Charters offers several booking and travel features intended to simplify the customer experience.

    The company provides 24-hour availability, online booking, quote requests and flexible payment options. Baby-seat options are also available for families travelling with young children.

    Its broader service model focuses on door-to-door transportation, allowing customers to arrange journeys according to their pickup and destination requirements.

    Travellers interested in Swan Valley Tours can visit the company’s website to explore available transport services and request a quote for their planned journey.

    Supporting Tourism and Private Travel Across Perth

    The introduction of Swan Valley Tours reflects Elegant Charters’ continued focus on providing transportation solutions for visitors and residents across the Perth metropolitan area.

    As regional tourism destinations remain an important part of Western Australia’s visitor experience, accessible private transportation can help travellers plan journeys that accommodate their schedules, group sizes and individual preferences.

    Through its combination of chauffeur-driven vehicles, group transport options and personalised travel arrangements, Elegant Charters aims to make regional sightseeing and private travel more convenient.

    Company Background

    Elegant Charters is a Perth-based passenger transportation and chauffeur service provider operating from Southern River, Western Australia. The company offers airport transfers, private chauffeur services, corporate transportation, tours, wedding transport, event transfers and group travel.

    Its fleet includes sedans, SUVs, multi-passenger vehicles, minibuses and maxi cabs designed to accommodate a range of passenger requirements. Additional services include FIFO transportation, cruise transfers, long-distance journeys and family travel with baby-seat options.

    Customers can access booking information and request transportation quotes through the company’s website.

    Executive Statement

    Insert an approved statement from an Elegant Charters representative about the introduction of Swan Valley Tours, the importance of convenient regional transportation and the company’s commitment to passenger comfort and service reliability.

    Looking Ahead

    Elegant Charters plans to continue developing its transportation services to address the changing requirements of Perth residents, business travellers and visitors to Western Australia.

    The addition of Swan Valley Tours further expands the company’s private travel options, providing another way for individuals and groups to arrange chauffeur-driven transportation to destinations beyond the Perth metropolitan area.

    Media Contact

    Elegant Charters
    Location: Southern River, Western Australia
    Phone: +61 458 655 640
    Website: https://elegantcharters.com.au/

  • Municipal Stump Removal Services Now Available in Cincinnati

    Municipal Stump Removal Services Now Available in Cincinnati

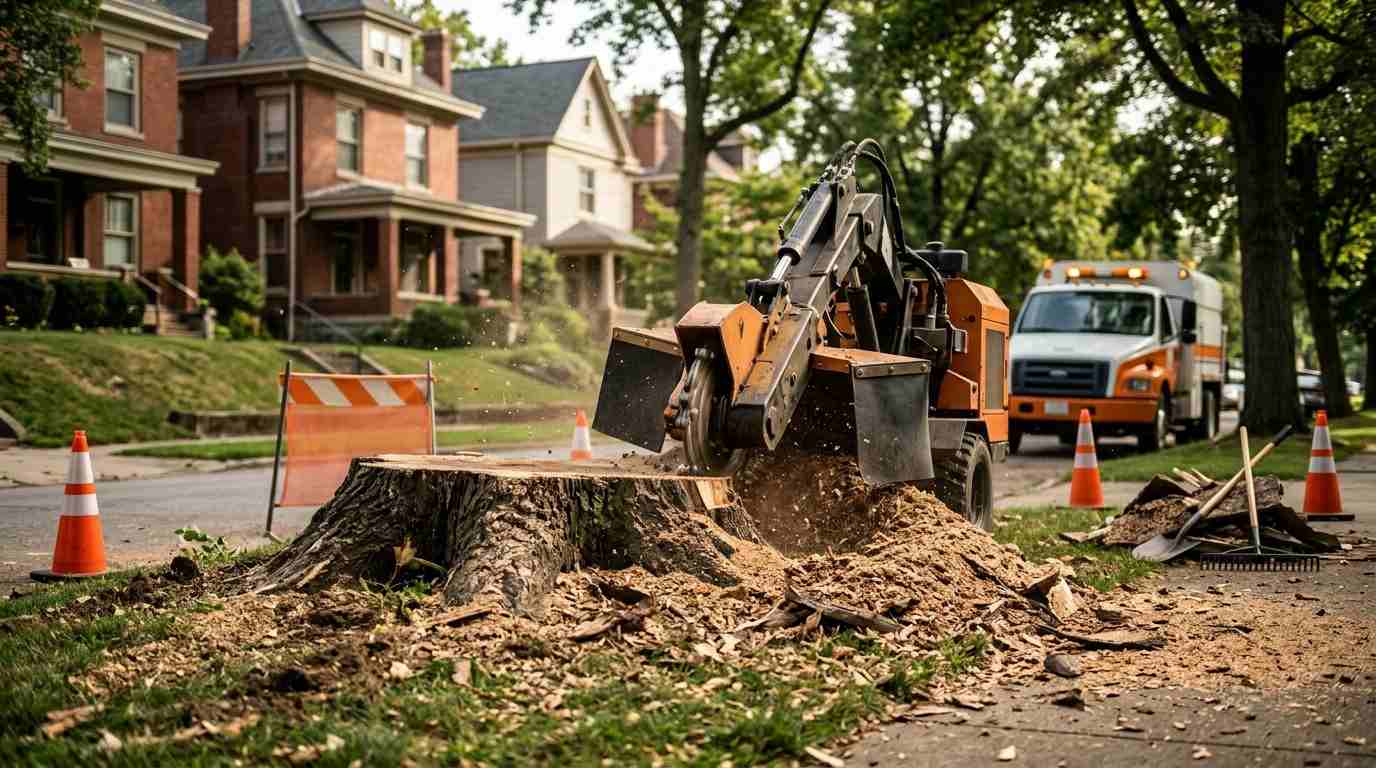
    Valentine Services – Stump Grinding has announced the availability of municipal stump removal services in Cincinnati, Ohio, expanding its professional stump grinding capabilities to address the needs of municipal properties, public spaces and other community-managed areas. The service is intended to help municipalities manage unwanted tree stumps, exposed roots and potential tripping hazards across public and maintained properties.

    Tree stump removal is an ongoing maintenance consideration for municipalities responsible for parks, sidewalks, public grounds, roadside areas and other community spaces. Remaining stumps can interfere with routine landscaping, create obstacles for pedestrians and complicate property maintenance. Professional stump grinding provides a method for addressing these issues without requiring complete excavation of every tree stump.

    Valentine Services – Stump Grinding is responding to these maintenance needs by making its stump grinding and removal capabilities available for municipal projects in the Cincinnati area. The company provides stump grinding services designed to remove unwanted stumps below ground level while addressing surrounding surface roots and managing the resulting wood chips.

    Addressing Municipal Property Maintenance Challenges

    Municipal property managers and public works departments regularly encounter tree maintenance challenges following tree removals, storm damage and routine landscape management. Leftover stumps can occupy usable space, interfere with mowing operations and present potential safety concerns in areas with pedestrian activity.

    Municipal stump grinding offers an approach to clearing these obstacles while supporting ongoing property maintenance. Depending on site conditions and project requirements, grinding can help prepare affected areas for landscaping, turf restoration or other future uses.

    Company Expands Its Service Capabilities

    Valentine Services – Stump Grinding brings its experience in residential and commercial stump grinding to municipal property maintenance projects. The company serves Cincinnati and surrounding communities in Ohio and Northern Kentucky, providing services for property owners, businesses, contractors and other clients.

    Its service capabilities include below-grade stump grinding, surface root management, large stump removal, wood chip cleanup and site restoration. Additional restoration options include topsoil and seed applications to help prepare disturbed areas for future lawn growth.

    The company also emphasizes careful equipment access and protection of surrounding property during stump grinding operations.

    Municipal Stump Grinding Services in Cincinnati

    The municipal stump Cincinnati service is intended to address stump removal requirements across a range of property types and site conditions. Project needs may vary depending on stump dimensions, root systems, surrounding structures, accessibility and the intended use of the cleared area.

    Available capabilities include:

    • Municipal and public-property stump grinding
    • Removal of large and unwanted tree stumps
    • Surface root grinding and management
    • Below-grade stump grinding
    • Wood chip cleanup and removal options
    • Site leveling and restoration preparation

    Municipalities and property managers can contact the company to discuss individual projects, site requirements and estimates.

    About Valentine Services – Stump Grinding

    Valentine Services – Stump Grinding provides professional stump grinding and stump removal services throughout Cincinnati, Ohio, and Northern Kentucky. The company works with homeowners, businesses, property managers, contractors and other property stakeholders to remove unwanted tree stumps and surface roots.

    Additional details are available at: https://share.google/FhICefWA6JHjY7oiz

    Its services include residential and commercial stump grinding, large stump removal, root grinding, chip cleanup and site restoration. The company serves Cincinnati, Blue Ash, Mason, West Chester, Fairfield, Loveland, Hamilton and surrounding Ohio communities, as well as Florence, Covington, Erlanger, Burlington, Hebron and other Northern Kentucky locations.

    Valentine Services is licensed and insured and has served the Cincinnati and Northern Kentucky region since 2010.

    Looking Ahead

    As municipalities continue to maintain public landscapes and address the challenges associated with aging or removed trees, professional stump grinding can play a role in keeping managed properties accessible and suitable for future landscaping.

    Valentine Services – Stump Grinding plans to continue supporting property maintenance needs throughout Cincinnati and Northern Kentucky through its residential, commercial and municipal stump grinding capabilities.

    Municipal representatives, contractors and property managers interested in municipal stump removal services can contact the company at 513-570-4626 or visit https://www.513stumps.com/ for additional information.

    Media Contact

    Valentine Services – Stump Grinding
    Email: bikemanjrv95@gmail.com
    Phone: 513-570-4626
    Website: https://www.513stumps.com/

  • How Netflix, Spotify and YouTube Premium Bill Your Card (and Why Renewals Fail)

    How Netflix, Spotify and YouTube Premium Bill Your Card (and Why Renewals Fail)

    Your card worked when you signed up, and it worked last month. Then this morning you see “Your payment was declined” and a banner asking you to update your payment details. Streaming renewals fail for a handful of mechanical reasons, and once you know how these services bill, most of them take minutes to fix.

    Quick answer

    1. Check the basics the service compares: expiry date, security code and billing postal code.

    2. Make sure the card is enabled for online, recurring and (if needed) international payments.

    3. Make sure the balance covers the charge on the billing date, especially on a prepaid or debit card.

    4. If you pay through an app store, carrier or bundle, fix it there, not on the service’s site.

    How streaming billing works

    Every major streaming service uses the same basic model.

    At signup, you enter a card, and the service checks it. That may be a $0 verification or a small authorization that’s later released, and in many regions the issuer may ask for a 3D Secure confirmation. You also agree that the service can store the card and charge it on a schedule.

    On each billing date, the service charges the stored card as a merchant-initiated transaction. You don’t take part, and there’s usually no 3D Secure step, because your consent at signup covers it. The charge is normally in the currency of the country your account is registered in.

    If you pay through a partner (an app store, a mobile carrier, a TV or internet bundle), the partner bills you and the streaming service only sees whether the partner says you’ve paid. A declined card in that setup is a problem with the partner’s billing, not the streaming service’s.

    That’s why a card can pass at signup and fail later: the renewal is a different kind of transaction, on a different day, and your issuer, your balance or your card settings may have changed in between.

    What each service says about cards and failed payments

    The three services publish their own rules. Here’s what their help pages say, as checked on 25 Oct 2026:

    NetflixSpotifyYouTube Premium
    When you’re billedMonthly, on the date you signed upMonthly, on your plan’s renewal dateMonthly, on your membership’s billing date
    Card requirements statedVisa, Mastercard and Amex cards “must be enabled for recurring e-commerce transactions”; prepaid cards with those logos are accepted; virtual cards are accepted “in select markets”; you may need to enable international transactionsCard must be enabled for “foreign, secure online, and recurring purchases”Expired cards and incorrect billing addresses are named as common causes of failure
    If a renewal failsFix the details and retry the charge from your accountYou don’t lose Premium right away; Spotify tries again “over the next few days”You get an email and 3 days to fix it while payment is retried; then the membership shows as “Paused” for 30 days
    Where to fix itAccount page, or your partner if billed through oneAccount page, under your planyoutube.com/paid_memberships or Purchases and memberships in the app

    If Spotify’s retries keep failing, the account loses Premium and moves to the free tier [VERIFY: Spotify’s official wording on what happens after retries fail]. Netflix’s help pages don’t publish a retry schedule, so don’t count on one.

    The six reasons renewals fail

    1.  Not enough balance on the billing date. On a debit or prepaid card, the charge is declined as insufficient funds (decline code 51) if the money isn’t there when the service tries. The service’s clock decides the time, so “the 15th” may mean late on the 14th where you live.

    2.  An expired or replaced card. A new expiry date or card number means the stored details are out of date (an expired card is code 54). Some banks pass new details to merchants automatically; many don’t.

    3.  Card settings. Many banking apps let you switch off online, recurring or international payments. Netflix and Spotify both say the card must allow these. If your bank blocks recurring payments by default, the renewal fails even with money in the account.

    4.  A billing details mismatch. Netflix asks you to check the expiry date, security code and billing postal code. If the postal code doesn’t match what your issuer holds, an address check can fail.

    5.  Card type or country. Some cards aren’t accepted in some markets. Netflix, for example, accepts prepaid cards with the right logos, but virtual cards only in select markets. A card issued in another country may also trigger your issuer’s cross-border rules.

    6.  A generic issuer decline. “Do not honor” (code 05) means the issuer refused without saying why, often because its fraud model flagged the charge. Only the issuer can tell you more.

    A note on country: each service decides your account’s country from its own signals, and that sets the price, catalog and accepted payment methods. Your card can’t change it. Using a VPN or switching regions to get a cheaper price breaks these services’ terms and can get the account closed.

    Fixing a failed renewal: step by step

    1.  Read the exact message in your account or email. “Update your payment method” and “your bank declined” point to different fixes.

    2.  Check whether you’re billed through a partner. If so, go to that partner’s billing settings.

    3.  Compare the stored details with your card: number, expiry date, security code and billing postal code. Correct anything that differs.

    4.  Open your banking or card app. Make sure online, recurring and international payments are allowed, and that the card isn’t frozen or locked.

    5.  Check the balance covers the plan price, plus any tax.

    6.  Retry the payment from your account page, or wait for the service’s next automatic attempt.

    7.  If the issuer still declines, call it and ask why. If the card type isn’t accepted, switch to a different payment method.

    Using a prepaid virtual card for streaming

    Prepaid virtual cards suit streaming well when they’re accepted: you can put each service on its own card, cap what it can charge, and freeze it when you’re done. Check the service’s payment page for your country first, because acceptance varies.

    As one example, VCCBuy’s Netflix card guide covers using its prepaid virtual Visa or Mastercard for that service. You fund the card with USDT on TRC20, BEP20, ERC20, Polygon or Solana, or with USDC, ETH and several other coins (no BTC). The Visa Classic has a $9.99 issue fee, a 3% top-up fee and no monthly fee. If the service asks for 3D Secure at signup, the code appears in the dashboard for 10 minutes, with no phone number needed. You can also save a billing name and postal address on each card, which helps the address check, and freeze the card if you cancel.

    The limits matter here too. VCCBuy is not a bank, the cards are online only, deposits are checked before they are credited, and some services or markets decline prepaid or virtual cards. A VCCBuy card renews only if its balance covers the charge on the billing date, and the service’s own country and card rules always apply.

    Renewal checklist

    ☐  I know my billing date for each service, and I’ve noted it in my calendar

    ☐  Each card allows online, recurring and (if needed) international payments

    ☐  The billing postal code saved at each service matches my card

    ☐  Prepaid or debit balances cover each charge a few days early

    ☐  I’ve updated expiry dates after any card replacement

    ☐  I know which subscriptions are billed through an app store, carrier or bundle

    ☐  My account country is the country I actually live in

    FAQ

    Why did my card work at signup but fail at renewal? Signup was often a $0 or small verification and may have included your confirmation through 3D Secure. The renewal is a full-price, merchant-initiated charge on a later date. A low balance, a changed card setting, an expired card or an issuer fraud flag can each block it.

    How long do I have before I lose access? It depends on the service. YouTube Premium gives you 3 days while it retries, then pauses the membership for 30 days. Spotify retries over a few days before you lose Premium. Netflix doesn’t publish a timeline, so fix the payment as soon as you see the notice.

    Can I pay for Netflix with a prepaid or virtual card? Netflix says it accepts prepaid cards that carry the Visa, Mastercard or Amex logo, and virtual cards in select markets. If your virtual card is declined, Netflix suggests choosing a different payment method.

    Conclusion

    Streaming services bill a stored card on a schedule, and renewals fail when something about that card has changed since signup: its balance, its settings, its details or the issuer’s view of it. Check those in order and most declines take minutes to clear. Before your next billing date, run through the checklist and set a reminder to make sure each card is ready.

    About the author: [Author name] is a payments and fintech writer at VCCBuy (https://vccbuy.net/), where they cover virtual cards, card networks and spending stablecoins online. They write about recurring billing and why renewals fail, using each service’s own published rules.

    Disclosure: the author writes for VCCBuy, which is mentioned in this article.

  • Asher Movers Introduces Office Moving Services for Skokie Businesses

    Asher Movers Introduces Office Moving Services for Skokie Businesses

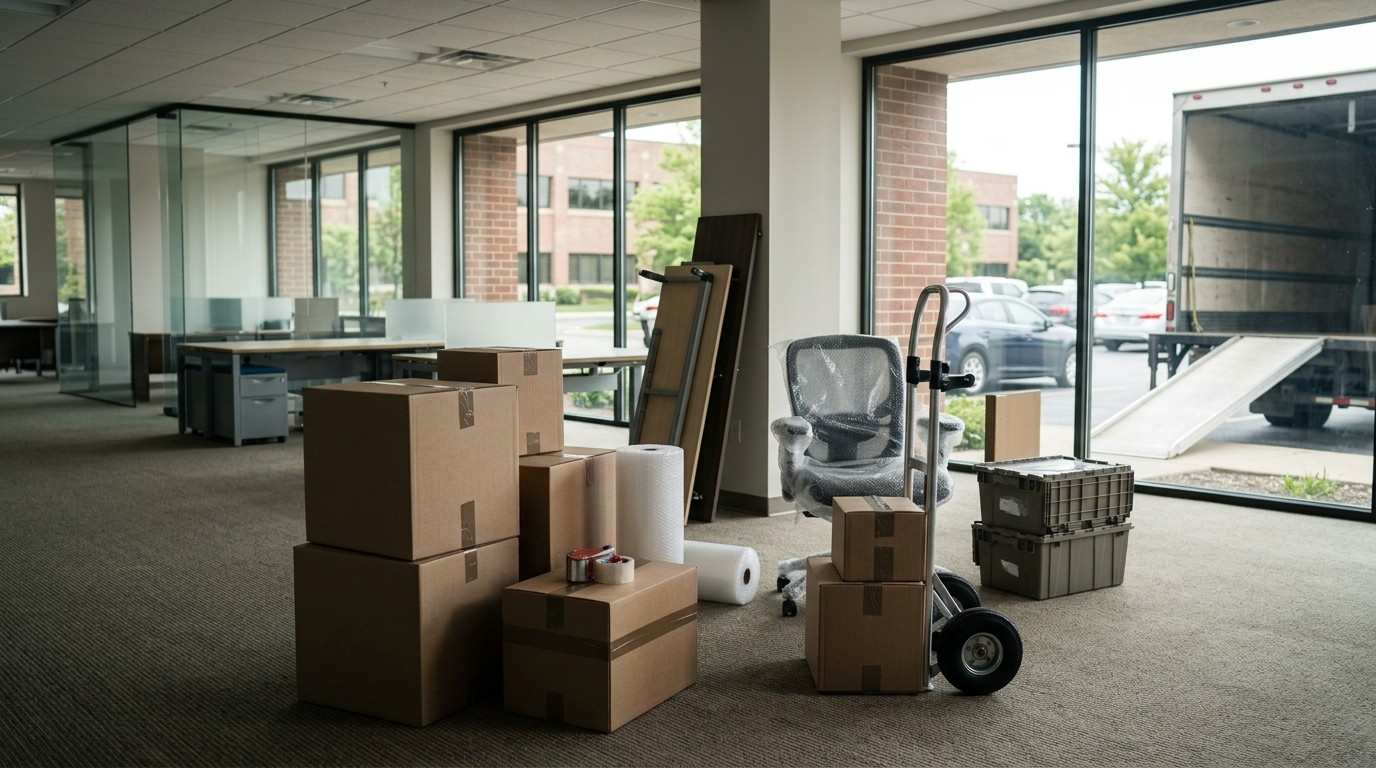
     Asher Movers Local & Long Distance has expanded its moving services to include office moving and business relocation support for organizations in Skokie and surrounding Chicago suburbs.

    The new service is designed to support businesses preparing for office relocations, whether they are moving to a larger workspace, transitioning to a new commercial property or reorganizing their existing operations. The company provides moving solutions tailored to the needs of businesses, with an emphasis on careful handling and coordinated relocation.

    Addressing the Challenges of Office Relocation

    Office moves can involve more than transporting furniture from one address to another. Businesses may need to coordinate the movement of desks, office equipment, files, supplies and other workplace items while minimizing disruption to normal operations.

    For small businesses and larger organizations alike, a relocation may also require planning around building access, scheduling and the specific requirements of the new workspace.

    Asher Movers’ expanded office moving service is intended to provide businesses with professional support throughout the physical relocation process.

    Asher Movers’ Response

    Asher Movers provides local and long-distance moving services for residential and commercial customers throughout Chicago and nearby suburbs. Its office moving service extends the company’s commercial relocation capabilities to businesses in Skokie.

    Additional details are available at: https://share.google/ARk5r1Acgk9hptlQg

    The company can assist with moving office furnishings, equipment and other workplace items as part of a customized relocation plan. Businesses can also coordinate additional services based on their moving requirements.

    Office Moving Services in Skokie

    Asher Movers offers a range of moving services that can support office relocation projects, including:

    • Office and commercial moving
    • Local business relocation
    • Long-distance moving
    • Packing services
    • Furniture and equipment transportation
    • Apartment and residential moving
    • Piano moving
    • Specialty moving services

    The company states that its movers are licensed and insured and serve homeowners, businesses, students and military families throughout the Chicago area.

    About Asher Movers Local & Long Distance

    Asher Movers Local & Long Distance is a Chicago-area moving company providing local moving, long-distance moving, commercial relocation, apartment moving, packing, piano moving and specialty moving services. The company serves Chicago and surrounding suburbs and provides customized moving solutions for residential and commercial customers.

    Executive Quote

    “Office relocations require careful planning and coordination because businesses are managing a move while continuing to operate,” said a representative of Asher Movers Local & Long Distance. “Our expanded office moving service gives Skokie businesses another option for managing the physical aspects of their relocation.”

    Looking Ahead

    Asher Movers plans to continue providing moving and relocation services to customers throughout Skokie, Chicago and surrounding communities. The company’s expanded commercial moving offering reflects its broader focus on supporting both residential and business relocation needs.

    Media Contact

    Asher Movers Local & Long Distance
    Email: info@ashermovers.com
    Phone: 773-638-4167
    Website: ashermovers.com

  • Honolulu Urgent Care Clinic Expands Laboratory Testing Services in Honolulu

    Honolulu Urgent Care Clinic Expands Laboratory Testing Services in Honolulu

    Honolulu Urgent Care Clinic has expanded its range of medical services to include laboratory testing, providing patients in Honolulu with access to diagnostic testing as part of a broader approach to convenient outpatient care.

    Opening Summary

    The new laboratory testing service complements the clinic’s walk-in and primary care offerings, giving patients access to testing alongside medical evaluations and other healthcare services. Laboratory testing can provide clinicians with information that may assist in evaluating symptoms, supporting diagnoses and guiding appropriate care.

    For residents and visitors in Honolulu seeking convenient medical attention, the addition of laboratory testing provides another service within the clinic’s existing healthcare setting.

    Addressing a Local Healthcare Need

    Access to timely medical evaluation can be important when patients need care for illnesses, injuries or symptoms that require assessment. In some cases, laboratory testing may be part of that evaluation.

    Honolulu Urgent Care Clinic provides walk-in medical care for a range of common health concerns, including minor illnesses and injuries, allergic reactions, cold and flu symptoms, infections, asthma, headaches, animal bites and insect stings. The clinic’s expanded laboratory testing services add diagnostic support to its existing range of outpatient healthcare offerings.

    Company Response

    With laboratory testing now included among its services, Honolulu Urgent Care Clinic continues to provide multiple healthcare options within one outpatient setting. The service is intended to support clinical evaluations when testing is appropriate based on a patient’s symptoms and medical needs.

    Additional details are available at: https://share.google/pxUUidmx8tz1OpLcm

    Laboratory testing may be used in connection with a healthcare provider’s assessment and should be interpreted in the context of a patient’s medical history, symptoms and other clinical findings.

    Service Details

    Honolulu Urgent Care Clinic’s healthcare services include laboratory testing as well as:

    • Walk-in urgent care
    • Primary care services
    • COVID-19 testing
    • Physical examinations
    • Immunizations and vaccinations
    • Occupational health services
    • Preventive care
    • Treatment for minor illnesses and injuries
    • Care for allergic reactions, respiratory symptoms, infections and other common conditions

    Laboratory testing availability and the specific tests appropriate for an individual patient may depend on the clinical evaluation and circumstances. Patients can contact the clinic directly for current service information.

    Company Background

    Honolulu Urgent Care Clinic provides convenient walk-in and primary care services in Honolulu, Hawaii. Its healthcare team treats a range of common illnesses, injuries and other medical concerns while also providing testing, physical examinations, immunizations, occupational health services and preventive care.

    The clinic serves Honolulu residents and visitors seeking same-day outpatient medical care and access to healthcare services in a convenient setting.

    Executive Quote

    “Laboratory testing can be an important component of a medical evaluation when clinically appropriate,” said a representative of Honolulu Urgent Care Clinic. “By offering laboratory testing alongside our existing urgent care and primary care services, we can provide patients with access to additional diagnostic services as part of their healthcare visit.”

    Future Outlook

    Honolulu Urgent Care Clinic plans to continue providing accessible outpatient healthcare services for residents and visitors in Honolulu. The addition of laboratory testing reflects the clinic’s ongoing effort to offer a broader range of medical services within its care setting.

    Patients seeking information about laboratory testing or other available services can contact Honolulu Urgent Care Clinic directly.

    About Honolulu Urgent Care Clinic

    Honolulu Urgent Care Clinic provides walk-in medical care and primary care services in Honolulu, HI. The clinic treats minor illnesses and injuries, allergic reactions, cold and flu symptoms, infections, asthma, headaches, animal bites, insect stings and other common medical concerns. Its services also include COVID-19 testing, physical exams, immunizations, vaccinations, laboratory testing, occupational health services and preventive care.

    Media Contact

    Honolulu Urgent Care Clinic
    Email: Hello@honoluluurgentcare.com
    Phone: 808-470-5555
    Website: https://honoluluurgentcare.com/

  • SAP CPI Integration Architecture: Components and Data Flow

    SAP CPI Integration Architecture: Components and Data Flow

    SAP CPI Integration provides a structured way to connect SAP applications, non-SAP applications, cloud platforms, and on-premise systems. It manages how business data moves between different systems and defines how messages are received, processed, transformed, routed, and delivered. SAP currently provides Cloud Integration as a capability within SAP Integration Suite on SAP Business Technology Platform (SAP BTP). It supports application-to-application (A2A), business-to-business (B2B), and business-to-government (B2G) integration scenarios across cloud, on-premise, and hybrid environments.

    The architecture of SAP CPI Integration is based on integration flows, also known as iFlows. An integration flow defines the sender, receiver, communication adapters, processing steps, and message flow required for an integration scenario. This architecture allows organizations to control data movement without requiring every application to communicate directly with every other application.

    What Is SAP CPI Integration Architecture?

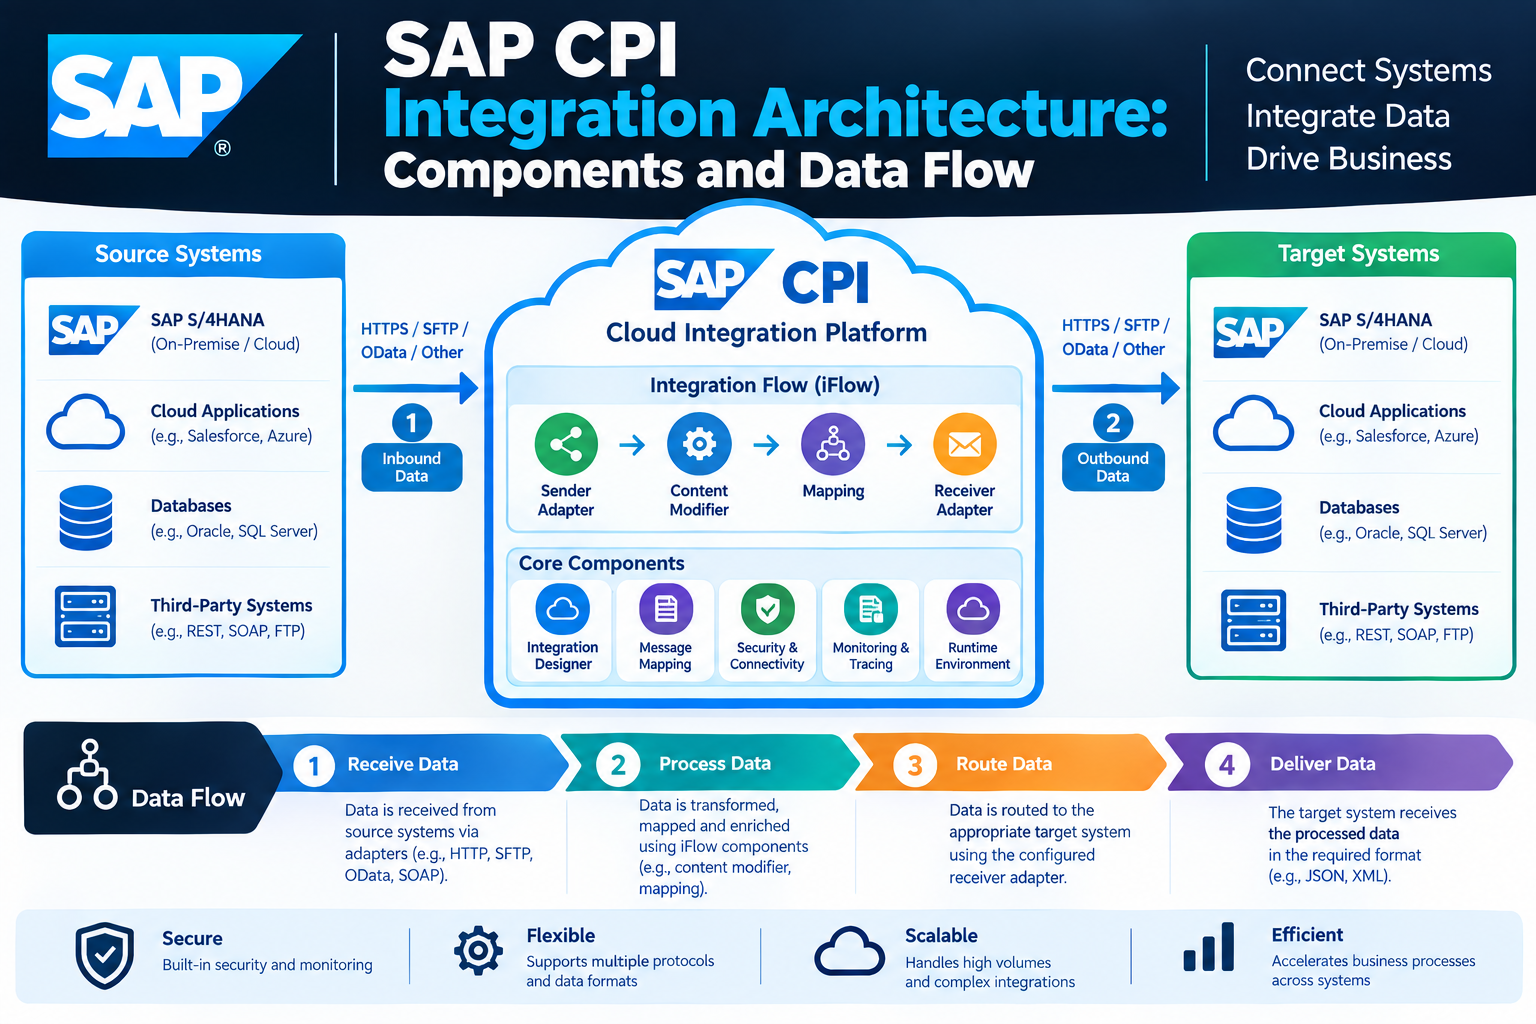
    SAP CPI Integration architecture describes the components and processing stages used to transfer data between connected systems. The architecture normally begins with a source or sender system, passes the message through an integration flow, processes the data according to defined rules, and sends the result to one or more receiver systems.

    An integration flow acts as the central processing model. SAP documentation explains that an integration flow specifies how a message is processed on the tenant. Developers can define senders and receivers, communication adapters, and message-processing steps within the graphical integration flow editor.

    For example, an organization may receive a sales order from an e-commerce platform. SAP CPI Integration can receive the order, validate its content, transform the data into an SAP-compatible structure, enrich the message with additional information, and send it to SAP S/4HANA.

    Main Components of SAP CPI Integration Architecture

    The architecture contains several important components that work together. Each component has a specific role in the movement and processing of business data.

    Integration Package

    An integration package provides a logical container for integration artifacts. It can contain integration flows and other artifacts used within an integration project. SAP documentation describes packages as a way to organize artifacts such as integration flows, value mappings, and APIs.

    For example, a company could create a package called Global_Sales_Integration and place multiple sales-related integration flows inside it. This organization makes integration content easier to manage and maintain.

    Integration Flow or iFlow

    The integration flow is the central design component of SAP CPI Integration. It describes how a message travels through the integration runtime.

    An iFlow can contain sender and receiver participants, adapters, processing steps, mapping, routing, filtering, scripts, and other integration components. Message flows connect the different elements and determine the processing sequence.

    A simple architecture can be represented conceptually as:

    Sender System → Sender Adapter → Integration Process → Processing Steps → Receiver Adapter → Receiver System

    This model can become more complex when the integration requires multiple receivers, conditional routing, enrichment, asynchronous processing, or error handling.

    Sender

    The sender is the system or application that starts or provides the message. It can represent an SAP application, cloud application, partner system, web application, or another connected source.

    For example, SAP S/4HANA could send an IDoc containing customer information, while an external application could send an HTTP request containing an order.

    Receiver

    The receiver is the system that receives the processed message. A receiver can be an SAP application, third-party application, database, SFTP server, web service, or another supported endpoint.

    A single integration scenario can contain different sender and receiver combinations depending on the business process.

    Adapters

    Adapters provide the technical connection between external systems and the Cloud Integration runtime. SAP documentation describes adapters as the mechanism used to specify the technical protocols for connecting senders and receivers to the integration flow.

    The appropriate adapter depends on the communication technology used by the connected system. Common technologies include HTTP, HTTPS, SOAP, SFTP, OData, IDoc, and other supported protocols.

    For example, an HTTPS sender adapter can receive a web request, while an SFTP receiver adapter can deliver a processed file to an external server.

    Message Processing in SAP CPI Integration

    After a message enters the integration flow, it can pass through multiple processing steps. These steps determine what happens to the message before it reaches the receiver.

    SAP Cloud Integration provides different processing capabilities for tasks such as transformation, routing, filtering, content modification, scripting, splitting, joining, and external service calls.

    A message may therefore follow a sequence such as:

    Receive → Validate → Transform → Enrich → Route → Deliver

    The actual sequence depends on the business requirement.

    Content Modifier

    A Content Modifier can change or add message content, headers, and properties during processing. It can be used when an integration needs to add information, modify message values, or prepare data for a later processing step.

    For example, an integration flow could add a business identifier or set a property before the message is routed to another system.

    Message Mapping

    Message mapping is used when the structure of the source message differs from the structure expected by the target system.

    For example, an e-commerce application may use:

    customer_name

    while the target SAP application expects a different field structure.

    A mapping can establish the relationship between source and target fields and apply functions where required. SAP Cloud Integration supports message mapping with supported source and target structures and provides mapping functions for transforming data.

    Router

    A Router allows the integration flow to select different processing paths based on defined conditions.

    For example, an order integration could route messages according to country:

    Germany → SAP S/4HANA Germany

    France → SAP S/4HANA France

    United Kingdom → UK Processing Flow

    This makes conditional processing possible within a single integration architecture.

    Filter

    A Filter can prevent unwanted messages or message content from continuing through a particular processing path. It is useful when only specific records or conditions should be processed.

    Script

    Scripts can provide custom processing logic when standard integration-flow steps are not sufficient. SAP documentation identifies script processing as a supported integration capability, including Java or Groovy-based scripting depending on the supported feature and scenario.

    Scripts should be used carefully because every processing step consumes tenant resources. SAP recommends designing integration flows with resource usage, resilience, and maintainability in mind.

    SAP CPI Integration Data Flow

    The data flow describes how a message moves from the source system to the target system. The message normally enters through a sender adapter and then passes through the processing steps defined in the integration flow.

    Consider an employee synchronization scenario.

    An HR application sends employee information to SAP CPI Integration through an HTTPS endpoint. The sender adapter receives the message and passes it into the integration process. A validation step checks the message, a mapping step converts the source structure into the required target structure, and a Router can determine the correct processing path. The receiver adapter then sends the transformed message to the target SAP system.

    The basic flow can be represented as:

    Source Application → Adapter → Integration Flow → Transformation → Routing → Receiver Adapter → Target Application

    This architecture separates business processing logic from the technical communication method.

    Synchronous and Asynchronous Data Flow

    SAP CPI Integration can support different processing patterns depending on the integration scenario.

    In a synchronous process, the sender expects a response during the same interaction. A request can be received, processed, sent to a receiver, and the resulting response can be returned to the sender.

    In an asynchronous process, the sender does not necessarily wait for the complete downstream processing to finish. Messaging and other integration patterns can be used when systems need to exchange information without maintaining a continuous synchronous interaction.

    The correct pattern depends on requirements such as response time, transaction behavior, system availability, message volume, and business process design.

    Security in SAP CPI Integration Architecture

    Security is an important part of the architecture because integration flows exchange business information between different systems.

    Authentication and authorization methods depend on the adapter and communication scenario. SAP Integration Suite supports different authentication options for integration-flow endpoints and connections to external systems.

    Secure communication protocols should be used when supported by the connected systems. SAP design guidance recommends encrypted protocols for secure communication with remote systems.

    Security can involve certificates, credentials, OAuth-based authentication, roles, authorization, and secure protocol configurations. The exact configuration should match the requirements of the sender and receiver systems.

    Error Handling and Monitoring

    A production integration architecture needs mechanisms for detecting and managing processing failures. An integration flow can fail because of invalid data, authentication problems, unavailable receiver systems, communication errors, mapping problems, or incorrect processing logic.

    SAP’s enterprise-grade integration guidance emphasizes resilience, graceful failure handling, supervision, resource management, and loose coupling. These characteristics help reduce the effect of failures on business processes.

    Monitoring is also important because integration teams need to determine whether messages were successfully processed. When an error occurs, developers can investigate the message-processing sequence and identify the stage where processing stopped.

    SAP CPI Integration Runtime and Deployment

    Designing an integration flow does not automatically make it active for business processing. The integration content must be deployed to the runtime environment.

    SAP explains that developers first design integration content and then deploy it. After deployment, the integration flows can operate and exchange data with connected sender and receiver systems. Cloud and on-premise systems can participate in these scenarios.

    This creates an important distinction between design time and runtime. Design time is where developers configure the integration flow. Runtime is where the deployed flow processes actual business messages.

    Naming Conventions for Integration Architecture

    Consistent naming is important when an organization manages many integration flows. SAP provides naming guidelines for integration flows, participants, channels, mappings, and other artifacts.

    For example, SAP documentation gives integration-flow naming patterns such as:

    Global_MM_PurchaseOrder

    and participant names such as:

    OP_ERP

    Channel names can use a pattern such as:

    HTTP_RCV_PurchaseOrderCreate

    Clear naming helps developers understand the purpose of an artifact without opening every configuration screen. SAP also recommends meaningful, generic names rather than technical or environment-dependent names.

    SAP CPI Integration Architecture Example

    Consider a retail company that receives orders from an online store and sends them to SAP S/4HANA.

    The online store acts as the sender. It sends an order message to an HTTPS endpoint. The sender adapter receives the request and passes it into the integration flow.

    The integration flow validates the incoming message and uses Message Mapping to convert the e-commerce structure into the format required by SAP S/4HANA. A Content Modifier can add required values, while a Router can send different orders through different processing paths.

    The receiver adapter then sends the transformed order to SAP S/4HANA. If the target system requires a response, the integration can process the response and return the required information to the original sender.

    This architecture avoids creating a direct custom connection between every application. Instead, Cloud Integration provides a controlled integration layer where connectivity, transformation, routing, security, and monitoring can be managed.

    Best Practices for SAP CPI Integration Architecture

    A well-designed architecture should keep integration flows understandable and maintainable. SAP’s enterprise-grade guidance emphasizes high availability, resilience, resource management, loose coupling, graceful failure handling, and readability.

    Keep integration flows focused on clear business responsibilities. Avoid unnecessary processing steps because each step can consume runtime resources. SAP specifically notes that processing steps consume resources such as CPU processing time and RAM, with some components having greater resource impact than others.

    Use secure authentication methods and encrypted communication protocols where supported. Keep credentials and security artifacts managed through appropriate platform mechanisms rather than embedding sensitive information directly into processing logic.

    Use meaningful names for packages, integration flows, channels, and mappings. Consistent naming makes large integration landscapes easier to operate and troubleshoot.

    AEO: What Is SAP CPI Integration Architecture?

    SAP CPI Integration architecture is the structure used to connect systems and control how messages are received, processed, transformed, routed, and delivered through Cloud Integration. Its main elements include sender systems, receiver systems, adapters, integration flows, message-processing steps, security configurations, and runtime deployment.

    The architecture can connect SAP and non-SAP systems across cloud, on-premise, and hybrid environments. Cloud Integration within SAP Integration Suite supports A2A, B2B, and B2G integration scenarios.

    GEO: How Does SAP CPI Integration Move Data?

    SAP CPI Integration moves data through a defined integration flow. A sender system submits a message through a configured adapter. The message then enters the integration process, where mapping, validation, routing, enrichment, filtering, scripting, or other processing steps can be applied.

    After processing, the message reaches the receiver adapter and is delivered to the target system. The exact data path depends on the integration flow design and the communication protocols used by the connected systems.

    For example:

    SAP S/4HANA → HTTPS/IDoc Adapter → Integration Flow → Mapping → Router → Receiver Adapter → Third-Party Application

    This structured architecture allows organizations to manage complex system-to-system communication through centralized integration logic.

    Frequently Asked Questions About SAP CPI Integration Architecture

    What is SAP CPI Integration architecture?

    SAP CPI Integration architecture defines the components and processing model used to connect systems and exchange business data. It includes senders, receivers, adapters, integration flows, processing steps, security, and runtime deployment.

    What is an iFlow in SAP CPI?

    An iFlow, or integration flow, is a graphical model that defines how a message is processed between connected systems. It specifies participants, adapters, message-processing steps, and message flows.

    What are the main components of SAP CPI Integration?

    The main components include integration packages, integration flows, sender and receiver systems, adapters, message-processing steps, mappings, routing logic, security configurations, and runtime services.

    What is the role of an adapter in SAP CPI Integration?

    An adapter provides the technical communication channel between the integration runtime and an external system. It defines how messages are exchanged using a supported communication protocol.

    How does data flow in SAP CPI?

    Data typically moves from a sender system through a sender adapter into an integration flow. The message is processed through defined steps such as mapping, validation, routing, or enrichment before a receiver adapter sends it to the target system.

    Can SAP CPI connect SAP and non-SAP systems?

    Yes. Cloud Integration supports integrations across SAP and non-SAP systems and can operate across cloud, on-premise, and hybrid landscapes.

    Why is message mapping used in SAP CPI?

    Message mapping is used to transform data from one message structure into another structure required by the target system. It is useful when source and target applications use different field names, structures, or data formats.

    Why is security important in SAP CPI Integration?

    Security protects data and communication between connected systems. Authentication, authorization, certificates, and encrypted communication can be used according to the adapter and integration requirements.

    What happens after an integration flow is designed?

    The integration flow must be deployed to the runtime environment before it can process messages in the operational scenario. After deployment, it can exchange data with configured sender and receiver systems.

    Conclusion

    SAP CPI Integration architecture provides a structured framework for connecting applications and managing business data across different environments. Its core architecture consists of sender and receiver systems, communication adapters, integration flows, processing steps, transformation, routing, security, and runtime deployment.

    The integration flow is the central element because it defines how messages move through the integration process. Developers can use mapping, routing, filtering, content modification, scripting, and other capabilities to implement different business requirements. SAP’s current Cloud Integration capability within SAP Integration Suite supports A2A, B2B, and B2G scenarios across cloud, on-premise, and hybrid landscapes.

    A clear architecture also helps organizations manage security, error handling, monitoring, performance, and maintainability. With appropriate design practices, SAP CPI Integration can provide a controlled integration layer between SAP applications, third-party platforms, and other enterprise systems.